Aokkef
medusalockerThis record tracks a ransomware attack claimed by the medusalocker group against Aokkef. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Aokkef.fr is an entity located in France within the Services sector, documented within this threat-intelligence index as a ransomware victim. The entity's classification reflects its inclusion in cybersecurity records tied to the medusalocker threat actor, a group historically associated with ransomware campaigns targeting service-oriented organizations. Details regarding specific attack vectors, operational impacts, or confirmed breach elements remain intentionally non-speculative per strict analytical protocols. This entry serves to catalog the entity's relationship to identified threats while maintaining factual neutrality. Aokkef.fr was listed as a ransomware victim associated with medusalocker.
Leak Screenshots
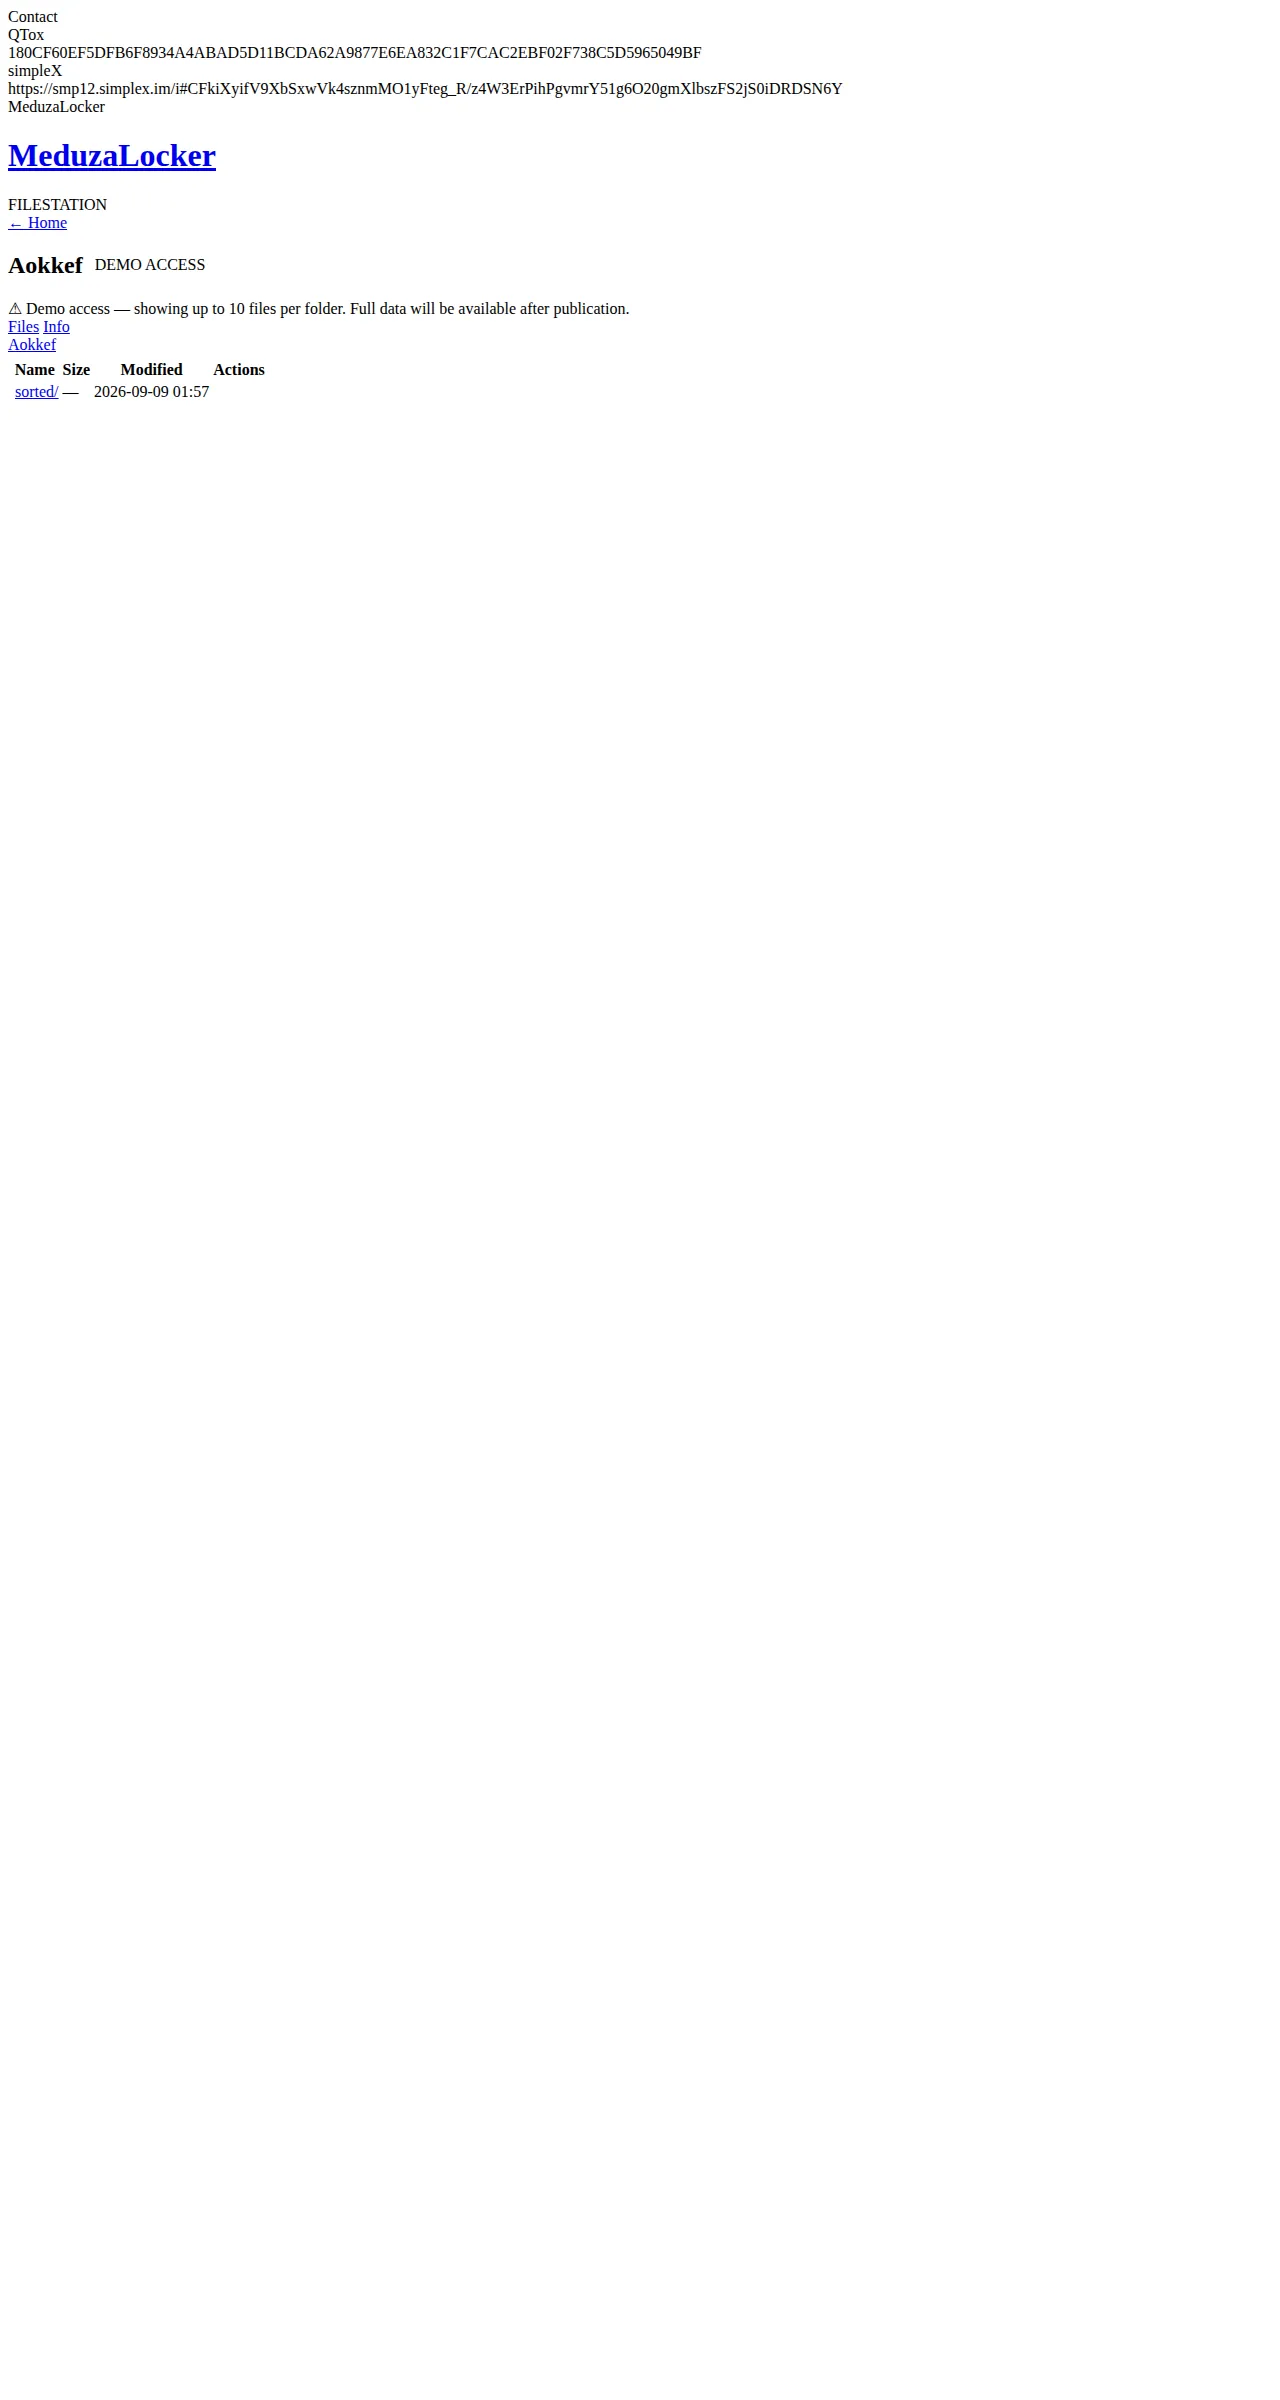
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-09-23. Verdict evidence: [H9] ⚠ Demo access — showing up to 10 files per folder. Full data will be available after publication.