This record tracks a ransomware attack claimed by the
thegentlemen group against
WABAG. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
0days open
t1 · Discovered
t2 · Pending
Business Category
Services
Indexed by Breach House
October 29, 2026
Leak Status
pending
checked 2026-10-29
Disclosed / Notified
Not disclosed yet
Attack Summary
WABAG is a company operating within the Services sector, headquartered in the Philippines. It provides professional and commercial services to clients and stakeholders within its regional and international markets. This entity is formally listed within the threat-intelligence index under the designation ransomware victim, associated with thegentlemen threat actor. The listing reflects its documented relationship to this actor within cybersecurity intelligence records. This classification supports threat analysts in tracking ransomware incidents across sectors and geographic regions without disclosing unverified incident details.
Leak Screenshots
1 CAPTURED
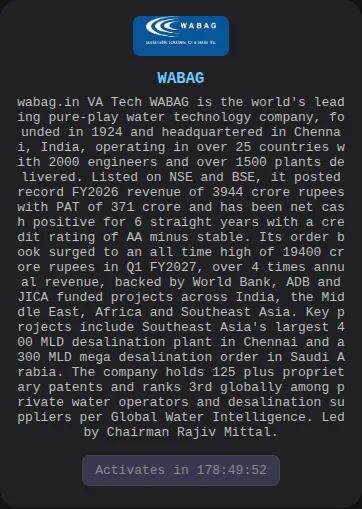
Captured directly from the operator's leak site by our collector, last checked 2026-10-29. Verdict evidence: [M1] Activates in 178:49:52
Showing the latest capture only
Unlock the daily capture history — up to 45 days of evidence.
Dark Web Exposure
Findings for wabag.in
— indexed by HaveIBeenRansom.
78
found in Infostealer logs
3,671+
found in Traditional breaches
245+
found in Ransomware leaks
[leakbase.io] servetel_in_Communication_Solutions_6gb.7z
Database World ROC · breach
••• emails
Hathway_BF_.7z.001
Database World ROC · breach
••• emails
indiamart.com 38m leads.rar
DBs Backup · breach
••• emails
IndiaMART_BF.7z
B F R e p o V 3 F i l e s · breach
••• emails
FORBESMARSHALL.COM
clop · ransomware
••• emails
B F R e p o V 3 F i l e s · breach
••• emails
TheUnderground - Reborn · breach
••• emails
+ 17 more leak sources locked
Leak volumes are locked
Sign in to reveal how many records each source exposed and the remaining 20 sources.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.