PITTSRAD
SpiralsThis record tracks a ransomware attack claimed by the Spirals group against PITTSRAD. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
pittsrad.net operates within the IT sector and is located in the United States. As a ransomware victim entity in this threat-intelligence index, it is documented in relation to the Spirals threat actor group. The listing provides contextual catalog information for security professionals monitoring ransomware activity, entity exposure, and associated adversary intelligence. This entry reflects the indexed relationship between the entity and Spirals without asserting unverified incident details such as breach confirmation, stolen data, ransom demands, or operational specifics. The description remains neutral and factual, adhering to the catalog’s purpose of documenting threat-related entity classifications.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector. Verdict evidence: listed on the leak site; no evidence of publication yet
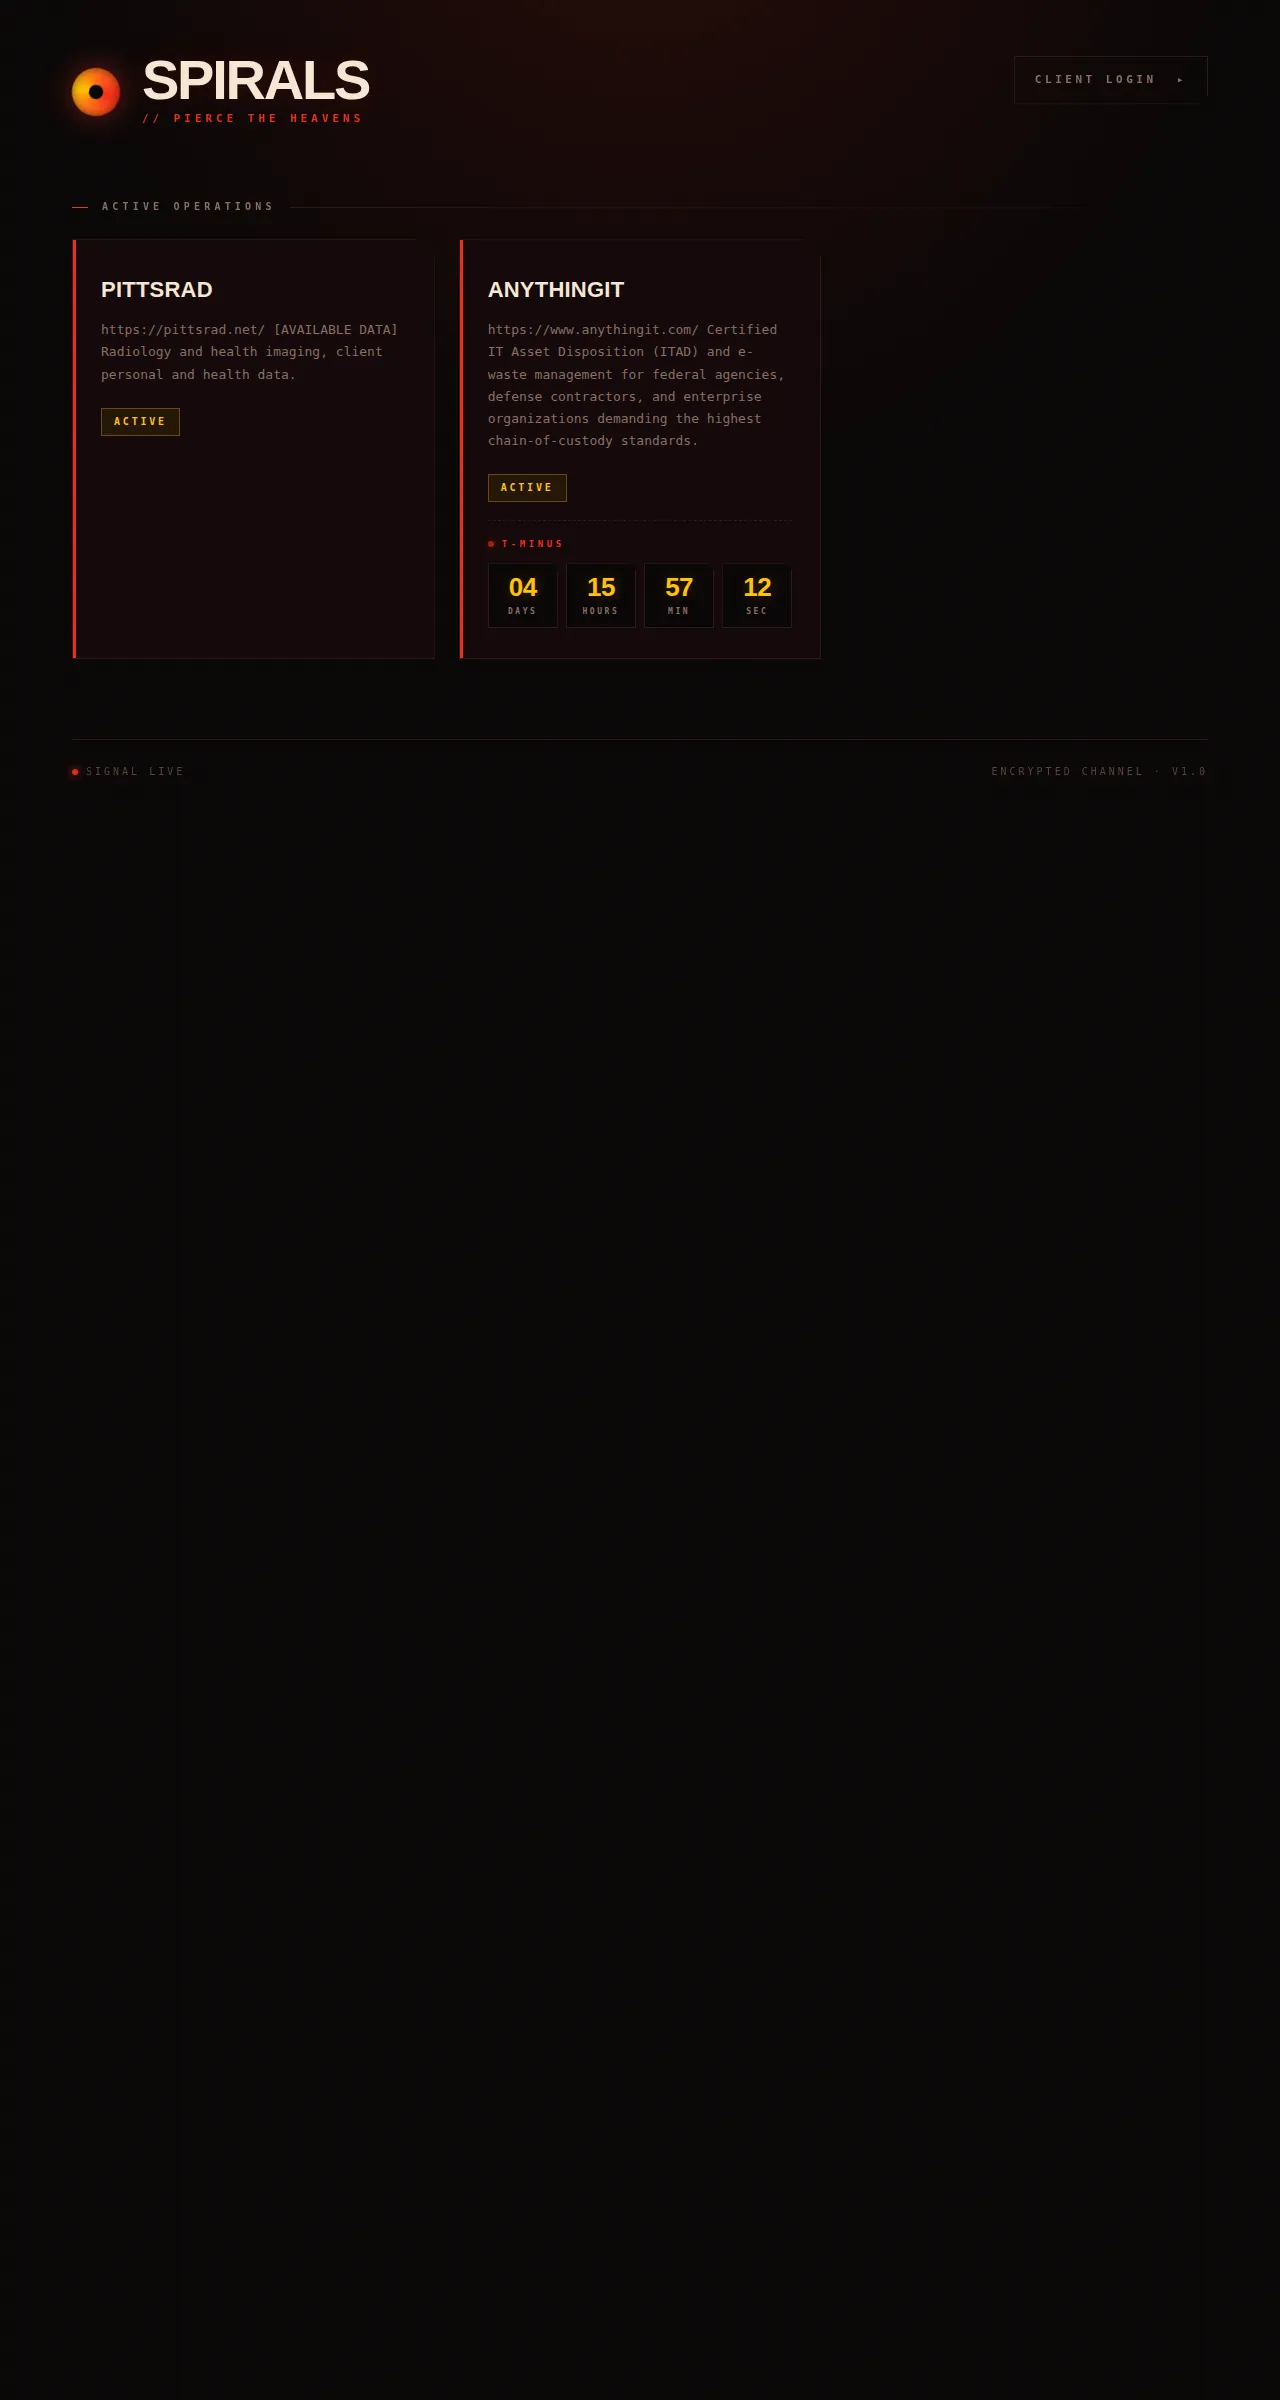
Capture history — 2 day(s) tracked. Content is locked.