This record tracks a ransomware attack claimed by the
spacebears group against
SGLA (Schwartz, Giannini, Lantsberger & Adamson). It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
0days open
t1 · Published
t2 · Pending
Business Category
Services
Indexed by Breach House
October 22, 2026
Leak Status
pending
checked 2026-10-22
Disclosed / Notified
Not disclosed yet
Attack Summary
www.sglacpas.com operates within the Services sector and is headquartered in the United States, delivering business and operational services aligned with its market positioning. The entity is cataloged in this threat-intelligence index specifically as a ransomware victim linked to the spacebears threat actor. This listing reflects the cybersecurity community's documented association between the organization and the activity attributed to spacebears. Analysis focuses on the entity's profile and the threat context rather than unverified incident details. The record serves to inform defenders and analysts about exposure patterns within the Services sector targeted by sophisticated ransomware campaigns.
Leak Screenshots
3 CAPTURED
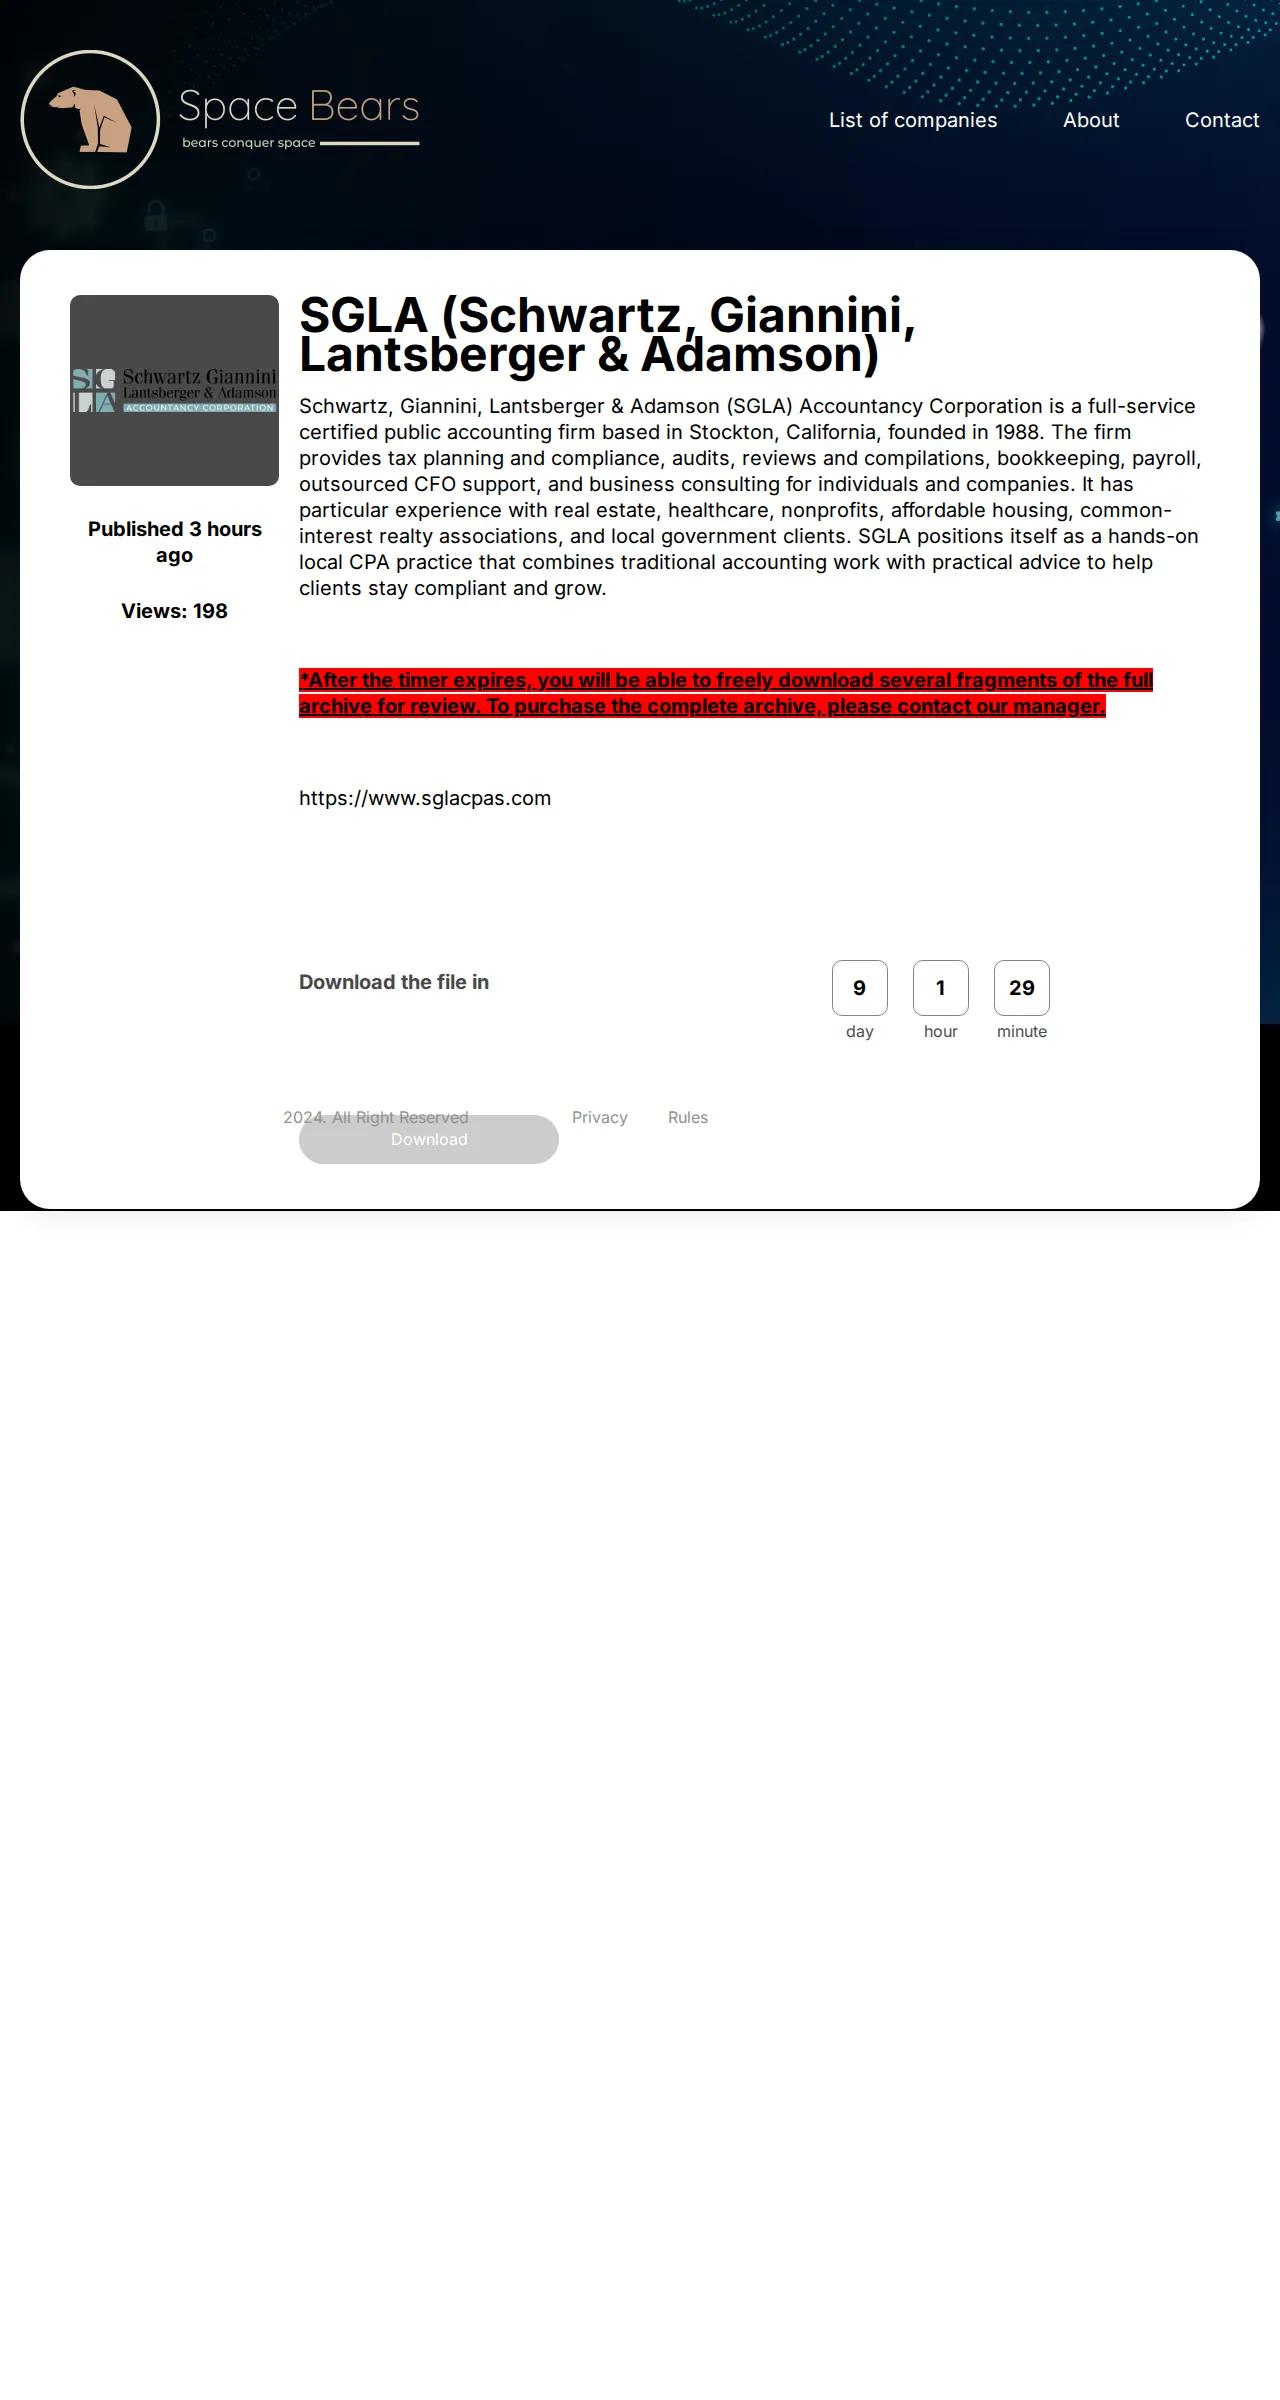
Captured directly from the operator's leak site by our collector, last checked 2026-10-22. Verdict evidence: [H7] 9 day 1 hour 29 minute
Proof files published by the operator —
2 image(s) harvested from this entry.
Content is locked; type and dimensions shown.
Showing the latest capture only
Unlock the daily capture history — up to 45 days of evidence, plus the 2 proof file(s) the operator published.
Dark Web Exposure
Cross-referenced against HaveIBeenRansom's dark-web index of ransomware leaks, breaches & infostealer logs.
0
found in Infostealer logs
0
found in Traditional breaches
0
found in Ransomware leaks
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
Full exposure is locked
See every breached email, the internal-vs-external split and each leak source behind this victim.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.