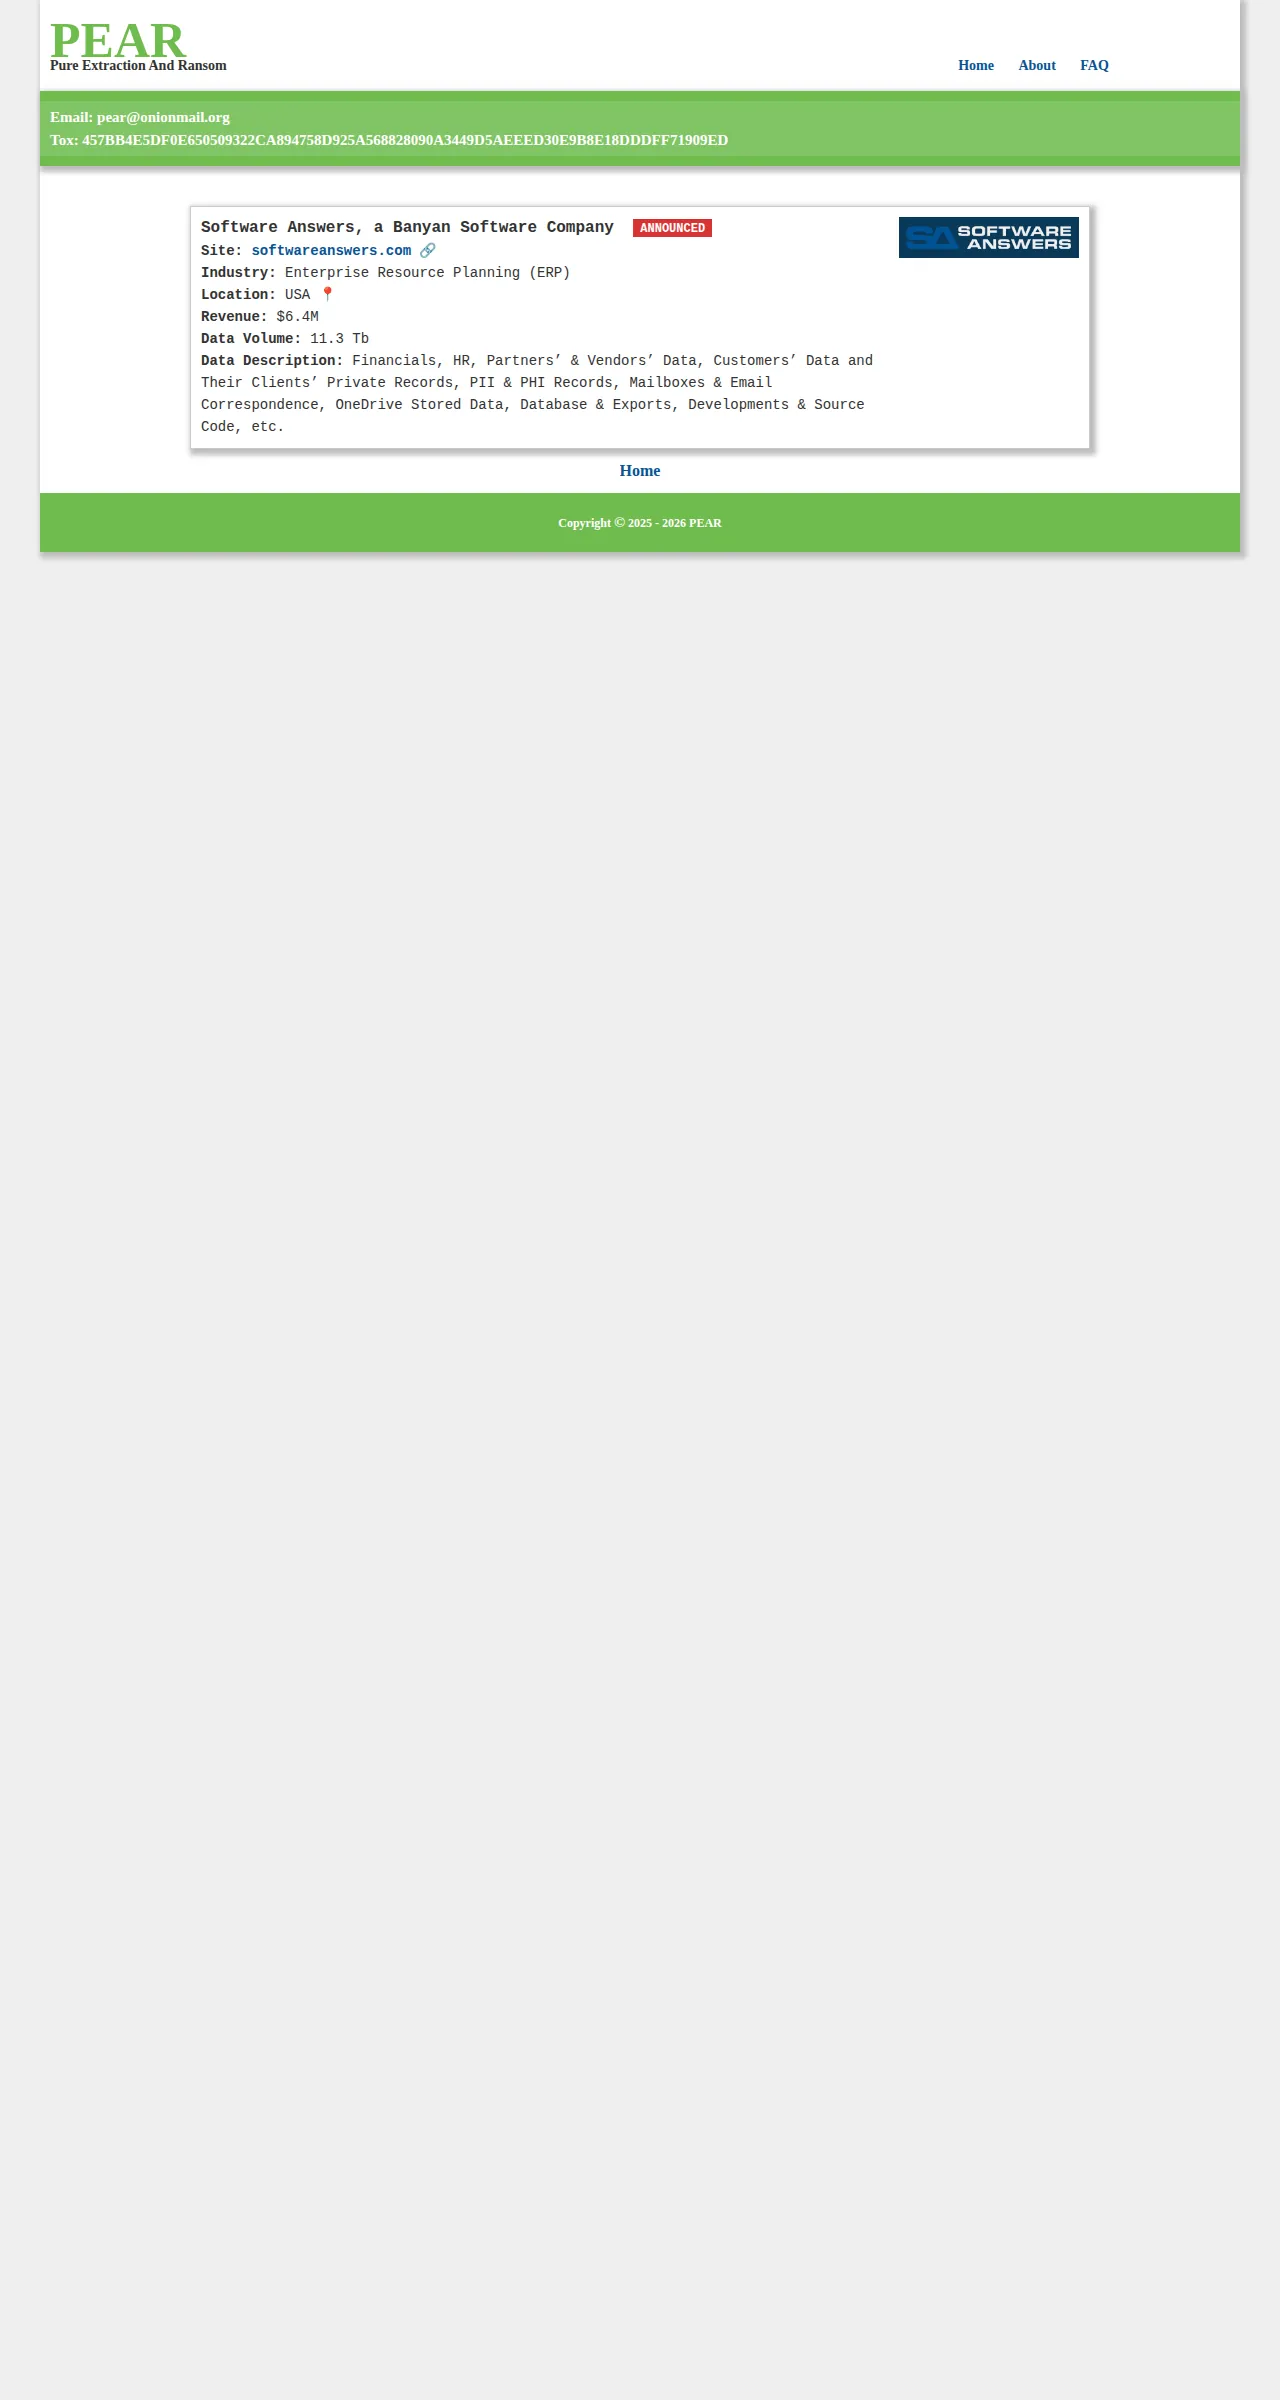
This record tracks a ransomware attack claimed by the
pear group against
Software Answers, a Banyan Software Company. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
17days open
t1 · Published
t2 · Pending
Indexed by Breach House
September 30, 2026
Leak Status
pending
checked 2026-09-30
Disclosed / Notified
Not disclosed yet
Attack Summary
softwareanswers.com operates within the IT sector and serves as a software answers platform providing technical support and information services. The entity is located in the United States. According to the threat-intelligence index, softwareanswers.com was formally listed as a ransomware victim associated with the threat actor pear. This designation reflects its inclusion within the ransomware victim category of the threat intelligence catalog. The listing type identifies the entity's relationship to the threat actor pear within this specific cybersecurity context.
Leak Screenshots
1 CAPTURED
Captured directly from the operator's leak site by our collector, last checked 2026-09-30. Verdict evidence: [H16] …re Answers, a Banyan Software Company ANNOUNCED
Showing the latest capture only
Unlock the daily capture history — up to 45 days of evidence.
Dark Web Exposure
Findings for softwareanswers.com
— indexed by HaveIBeenRansom.
0
found in Infostealer logs
281+
found in Traditional breaches
31+
found in Ransomware leaks
VerificationsIO_BF.7z.011
Kedr | Forum · breach
••• emails
pureincubation-com.7z.001
Database World ROC · breach
••• emails
Email Panther @dbworldcloud.7z
DBs w MTDT · breach
••• emails
Sysco Corporation
shinyhunters · ransomware
••• emails
Apollo.io DB 816millions.rar
Database World ROC · breach
••• emails
Database World ROC · breach
••• emails
+ 17 more leak sources locked
Leak volumes are locked
Sign in to reveal how many records each source exposed and the remaining 20 sources.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.