Website: superiortec.com
morpheusThis record tracks a ransomware attack claimed by the morpheus group against Website: superiortec.com. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Superiortec.com is an entity operating within the IT sector and headquartered in the United States. Publicly available information characterizes it as an organization within the technology domain, with no independently verified details regarding specific incident mechanics or operational scope. Within the threat-intelligence index under consideration, Superiortec.com is cataloged as a ransomware victim associated with the threat actor Morpheus. This listing reflects the entity's presence in cybersecurity intelligence records tied to that actor's activity. The description remains factual and neutral, avoiding speculation about data handling, breach confirmation, or unverified claims. Superiortec.com serves as a reference point for analyzing ransomware exposure patterns within the IT sector across US-based contexts.
Leak Screenshots
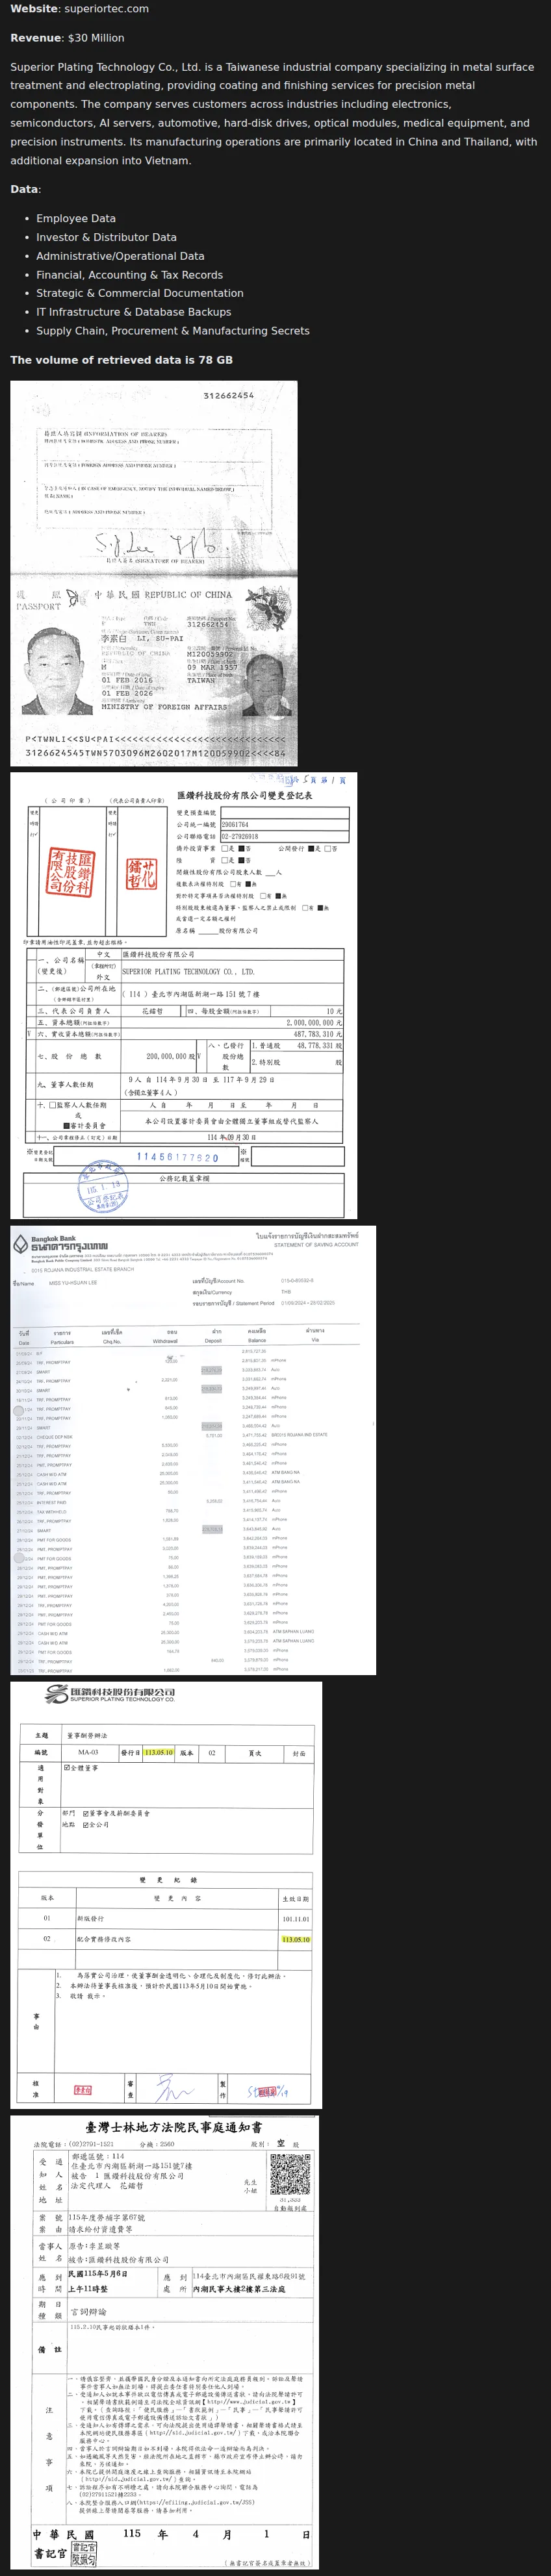
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-15. Verdict evidence: [M1] The volume of retrieved data is 78 GB