Home › All Victims › Concord Eye Center

Concord Eye Center

interlock

This record tracks a ransomware attack claimed by the interlock group against Concord Eye Center. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.

Window Zero

EXPOSURE GAP

Window Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.

0days open
t1 · Published t2 · Pending
Oct 12, 2026Not disclosed yet
Date
October 12, 2026
Indexed by Breach House
October 12, 2026
Leak Status
leaked
checked 2026-10-12
Leak download available Enterprise
Disclosed / Notified
Not disclosed yet
Victim ID
mY2j0BEgGnUT

Attack Summary

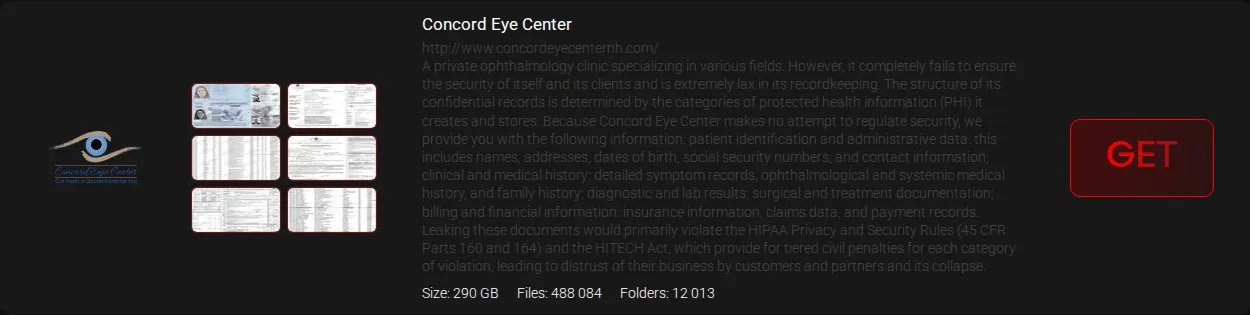
A private ophthalmology clinic specializing in various fields. However, it completely fails to ensure the security of itself and its clients and is extremely lax in its recordkeeping. The structure of its confidential records is determined by the categories of protected health information (PHI) it creates and stores. Because Concord Eye Center makes no attempt to regulate security, we provide you with the following information: patient identification and administrative data: this includes names, addresses, dates of birth, social security numbers, and contact information; clinical and medical history: detailed symptom records, ophthalmological and systemic medical history, and family history; diagnostic and lab results; surgical and treatment documentation; billing and financial information: insurance information, claims data, and payment records. Leaking these documents would primarily violate the HIPAA Privacy and Security Rules (45 CFR Parts 160 and 164) and the HITECH Act, which provide for tiered civil penalties for each category of violation, leading to distrust of their business by customers and partners and its collapse.

Leak Screenshots

1 CAPTURED

Captured directly from the operator's leak site by our collector, last checked 2026-10-12. Verdict evidence: [H15] Files: 488 084
Showing the latest capture only
Unlock the daily capture history — up to 45 days of evidence.

Dark Web Exposure

Cross-referenced against HaveIBeenRansom's dark-web index of ransomware leaks, breaches & infostealer logs.
0
found in Infostealer logs
0
found in Traditional breaches
0
found in Ransomware leaks
Emails exposed
••••
Internal
•••
External
•••
Distinct leaks
••
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
••••••••••••••••••••••••
•••••••••• · ••••••
••• emails
Full exposure is locked
See every breached email, the internal-vs-external split and each leak source behind this victim.
Want the complete picture — passwords, machines, full leak files? It's all searchable on HaveIBeenRansom.
Search this victim →
Visit Website Original Post View Group: interlock
Legal Disclaimer: This ransomware victim record reflects information published on the operator's leak site. Breach.house only records what the operators themselves publish in the open. We take screenshots of their public pages and keep the proof material they post there, so that a listing can be verified and its status tracked over time. We do not purchase data, we do not solicit or encourage its publication, we do not access any private system, and we do not alter anything we record. Nothing is offered for download here, and detailed content is not published on this page or anywhere else on the public site: access to it is restricted to vetted customers under contract, for incident response, due diligence and cyber-resilience work. Breach.house is not affiliated with, and does not act on behalf of, the operators who publish this material. If you represent an organisation or individual named here and want a record reviewed or removed, contact us and we will act on it.