Rheem Global
HelixThis record tracks a ransomware attack claimed by the Helix group against Rheem Global. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
Rheem Global is a United States-based company operating within the Manufacturing and Engineering sector, providing industrial valves, plumbing systems, and related engineering solutions for commercial and industrial applications. In the threat-intelligence index, Rheem Global is cataloged as a ransomware victim linked to the Helix threat actor. This listing reflects the entity's association with Helix within the ransomware incident context, without confirming specific breach details such as data stolen, records affected, ransom demands, or technical methodology. The entry serves to document the relationship between Rheem Global and Helix for cybersecurity professionals monitoring industrial-sector ransomware activity. Neutral treatment ensures factual representation aligned with available intelligence sources.
Leak Screenshots
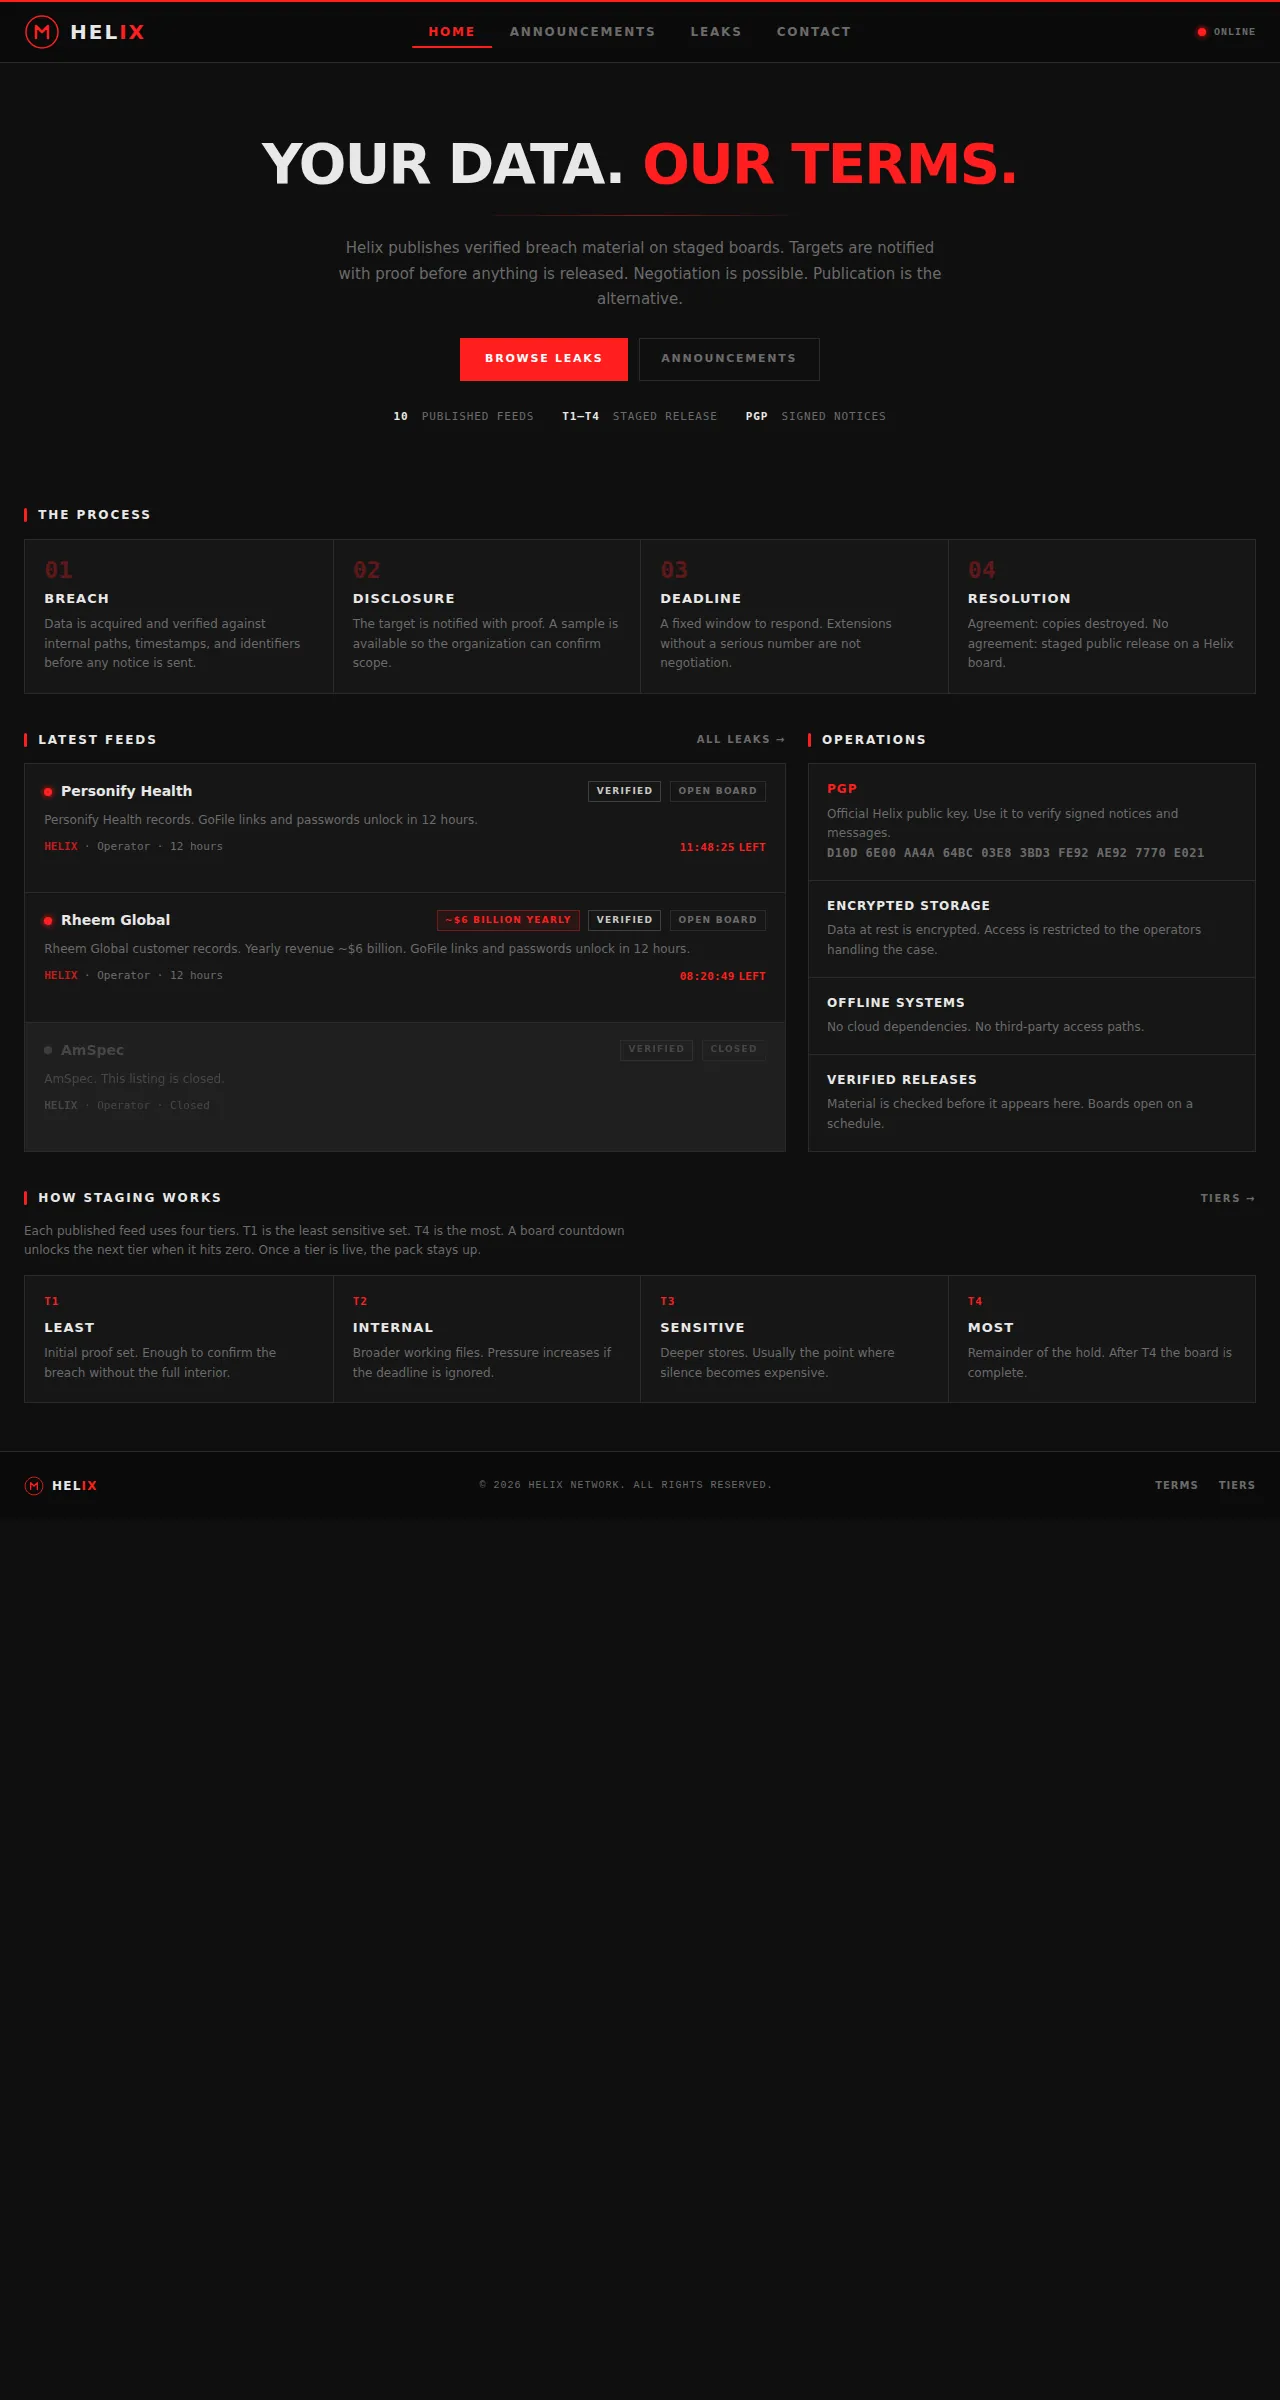
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-17. Verdict evidence: [H7] Each published feed uses four tiers. T1 is the least sensitive set. T4 is the most. A board countdown unlocks the next tier when it hits zero. Once a tier is live, the pack stays up.
Capture history — 2 day(s) tracked. Content is locked.