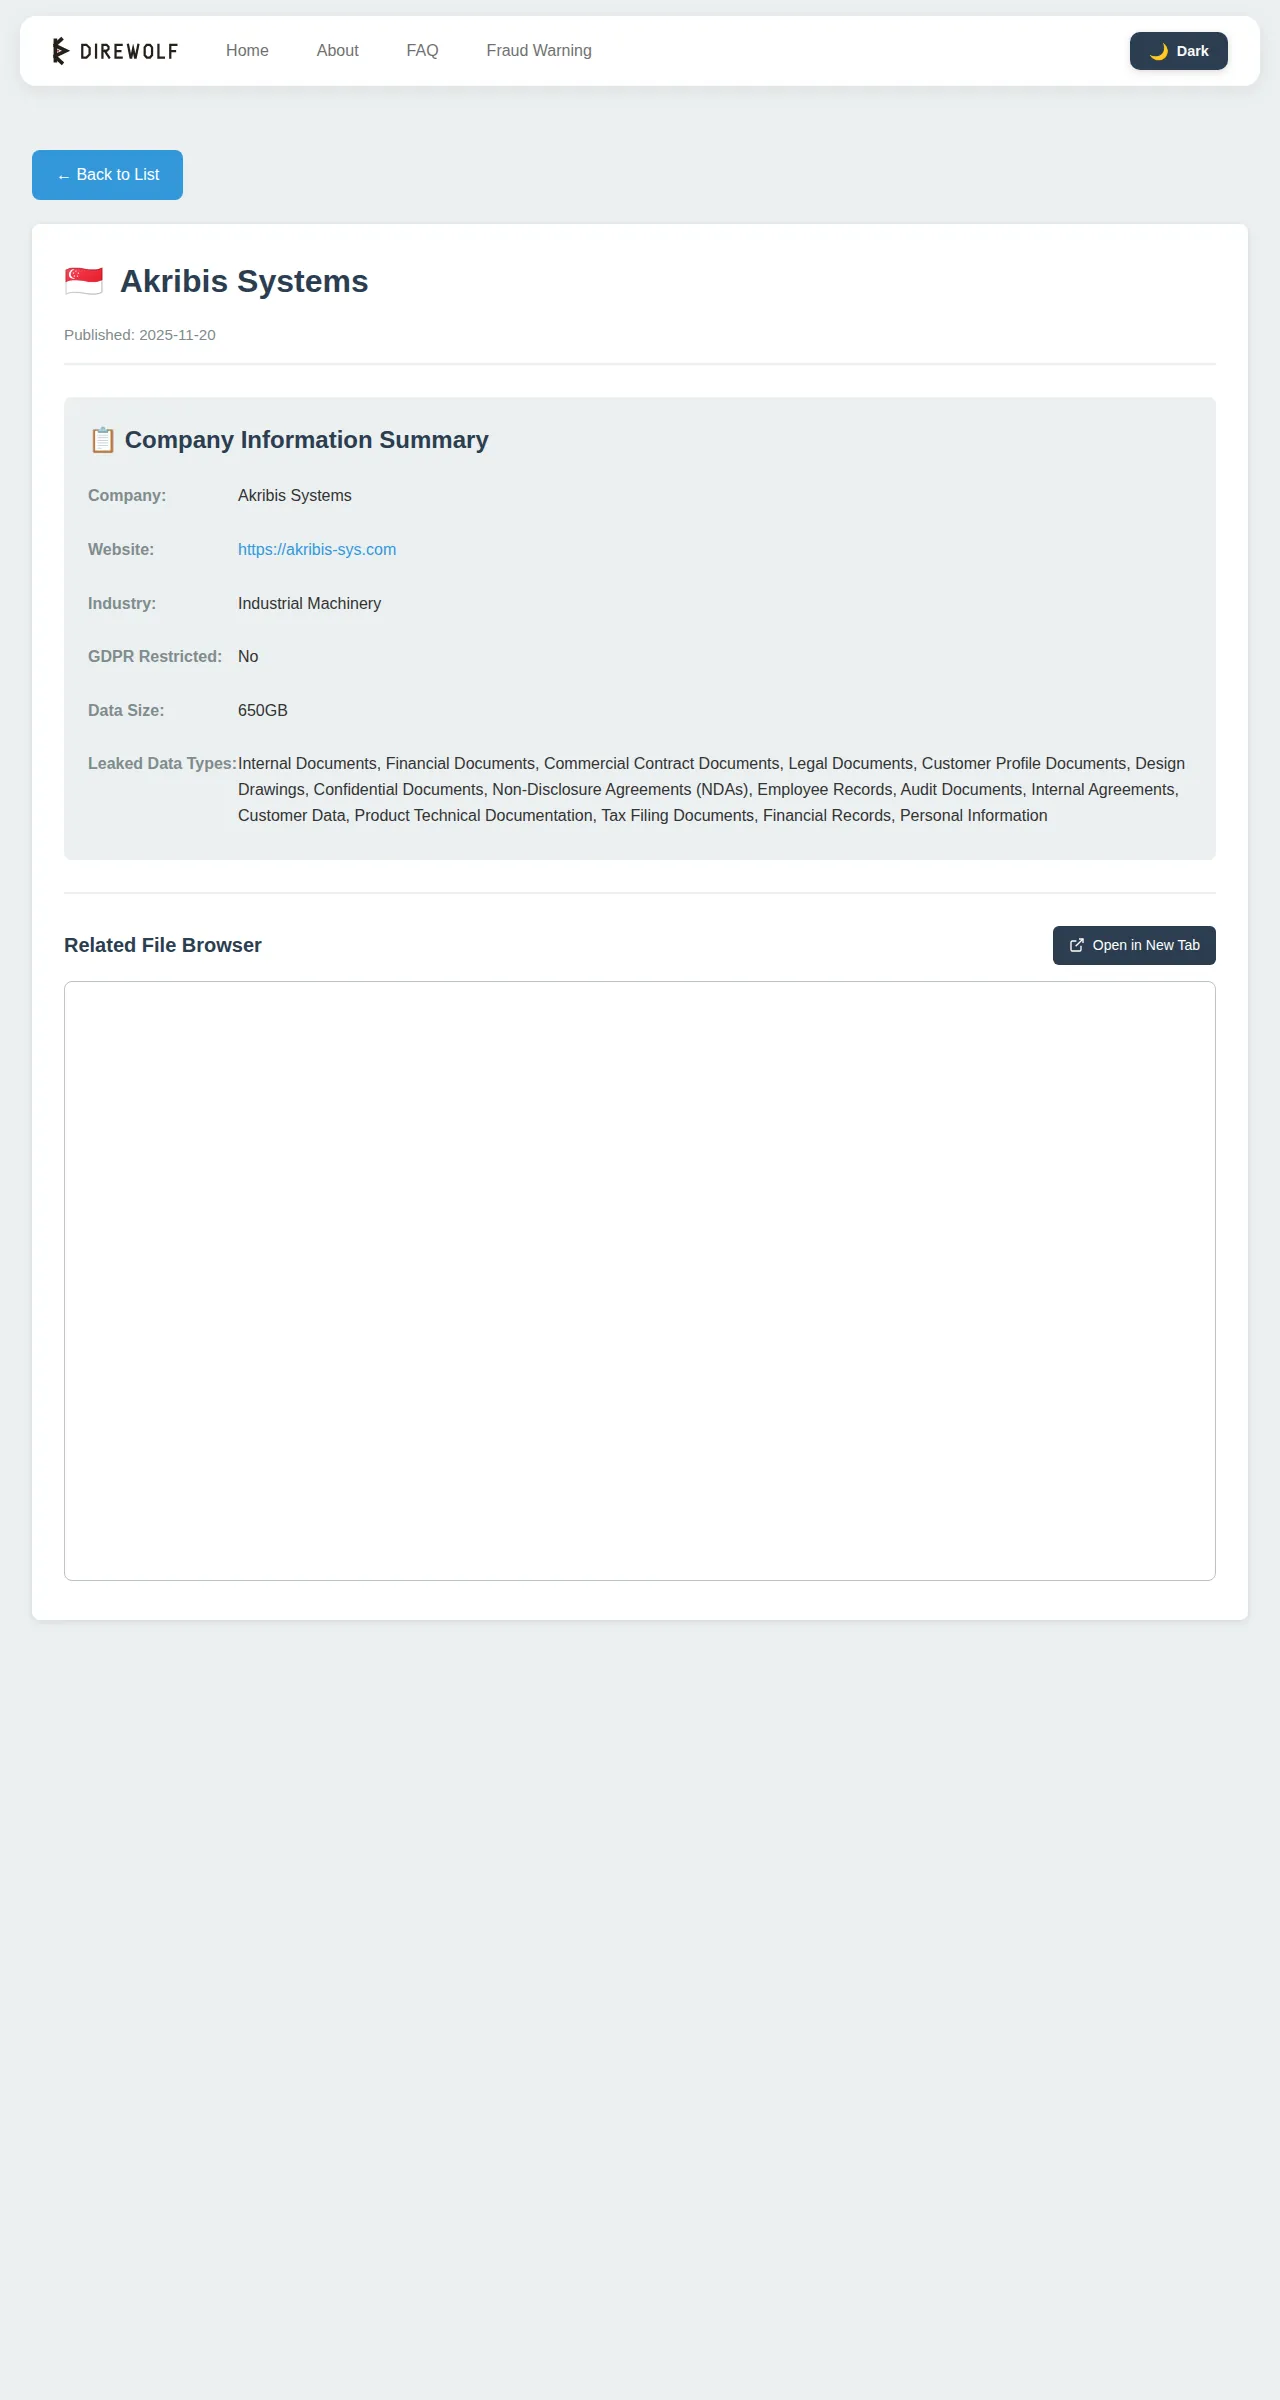
This record tracks a ransomware attack claimed by the
direwolf group against
🇸🇬
Akribis Systems. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
329days open
t1 · Published
t2 · Pending
Business Category
Manufacturing / Engineering
Indexed by Breach House
October 15, 2026
Leak Status
leaked
checked 2026-10-15
Disclosed / Notified
Not disclosed yet
Attack Summary
akribis-sys.com operates within the Manufacturing and Engineering sector, based in Greece (GR). The entity provides systems and technical services relevant to industrial operations, though specific internal capabilities are not disclosed here. It is cataloged in this threat-intelligence index under the listing type ransomware victim, with the associated threat actor Direwolf identified as the source of the security incident. The entry synthesizes publicly available intelligence regarding the entity's exposure to this threat actor within its operational domain. This record serves to inform defenders and analysts monitoring ransomware activity across industrial sectors in Greece and related regions. It was listed as a ransomware victim associated with direwolf.
Leak Screenshots
1 CAPTURED
Captured directly from the operator's leak site by our collector, last checked 2026-10-15. Verdict evidence: [M1] Published: 2025-11-20
Showing the latest capture only
Unlock the daily capture history — up to 45 days of evidence.
Dark Web Exposure
Findings for akribis-sys.com
— indexed by HaveIBeenRansom.
1
found in Infostealer logs
82
found in Traditional breaches
15
found in Ransomware leaks
pureincubation-com.7z.001
Database World ROC · breach
••• emails
Dropbox_BF.7z
B F R e p o V 3 F i l e s · breach
••• emails
148GB (17).txt
DBs Backup · breach
••• emails
Access Intelligence
play · ransomware
••• emails
MalindoAir_BF.7z
B F R e p o V 3 F i l e s · breach
••• emails
TheUnderground - Reborn · breach
••• emails
+ 17 more leak sources locked
Leak volumes are locked
Sign in to reveal how many records each source exposed and the remaining 20 sources.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.