University of New Mexico
BYODThis record tracks a ransomware attack claimed by the BYOD group against University of New Mexico. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
The University of New Mexico is a public research university in Albuquerque, New Mexico, United States, serving students and faculty across sciences, humanities, engineering, arts, and professional programs. Its mission encompasses higher education, research, community engagement, and regional academic and cultural contributions within the Education sector. In the threat-intelligence index, this entity is cataloged as a ransomware victim associated with the BYOD threat actor profile. The listing reflects its inclusion in ransomware incident tracking without confirming specific breach details, data scope, or operational impact. This neutral record supports cybersecurity monitoring, sector-specific threat analysis, and awareness of risks affecting educational institutions using bring-your-own-device configurations.
Leak Screenshots
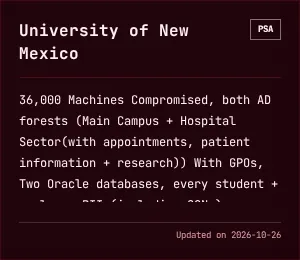
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-27. Verdict evidence: [M1] 36,000 Machines Compromised, both AD forests (Main Campus + Hospital Sector(with appointments, patient information + research)) With GPOs, Two Oracle databases, every student +
Capture history — 2 day(s) tracked. Content is locked.