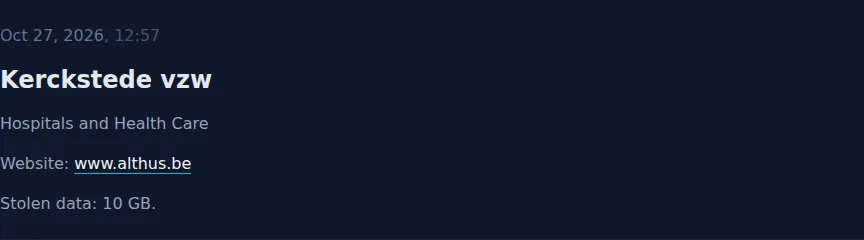
Kerckstede vzw
Booba ProjectThis record tracks a ransomware attack claimed by the Booba Project group against Kerckstede vzw. It collects the publicly disclosed attack details — sector, location and timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAPWindow Zero is the time the breach stayed in the open before anyone said so — the gap between when the attack was first discovered on the operator's leak site (t1) and when it was publicly disclosed (t2). The wider this window, the longer victims, staff and customers were exposed with no warning.
Attack Summary
althus.be is a company based in Belgium operating within the Services sector, providing professional and business-oriented offerings aligned with service-oriented industries. The entity has been cataloged in this threat-intelligence index under the listing type ransomware victim, with its association explicitly tied to the Booba Project threat actor. This designation reflects the cybersecurity classification of the organization within the Booba Project threat landscape, highlighting its status as an affected entity without disclosing unverified incident details. The entry serves as part of a comprehensive ransomware victim index designed to support threat analysis, risk assessment, and awareness across affected service-sector organizations in Belgium.
Leak Screenshots
1 CAPTUREDCaptured directly from the operator's leak site by our collector, last checked 2026-10-27. Verdict evidence: [H18] Stolen data: 10 GB.