This record tracks a ransomware attack claimed by the
akira group against
David L Wade & Assoc. It collects the publicly disclosed attack details — sector, location and
timeline — as published on the operator's leak site and indexed by Breach House.
Window Zero
EXPOSURE GAP
Window Zero is the time the breach stayed in the open before
anyone said so — the gap between when the attack was first discovered
on the operator's leak site (t1) and when it was publicly disclosed (t2).
The wider this window, the longer victims, staff and customers were exposed with no warning.
1day open
t1 · Published
t2 · Pending
Business Category
Services
Indexed by Breach House
November 08, 2026
Disclosed / Notified
Not disclosed yet
Attack Summary
dlwcpa.com operates within the Services sector and is based in the United States. Publicly available information describes the entity by its domain identity and sector classification, without disclosing specific operational details or confirmed incident specifics. The entity has been cataloged in this threat-intelligence index under the designation ransomware victim, with the associated threat actor or source identified as akira. This listing reflects the entity's inclusion in intelligence records tied to this actor's activity within the Services sector. No additional breach details, data claims, or financial impact are provided here, maintaining factual neutrality per strict reporting guidelines. It was listed as a ransomware victim associated with akira.
Leak Screenshots
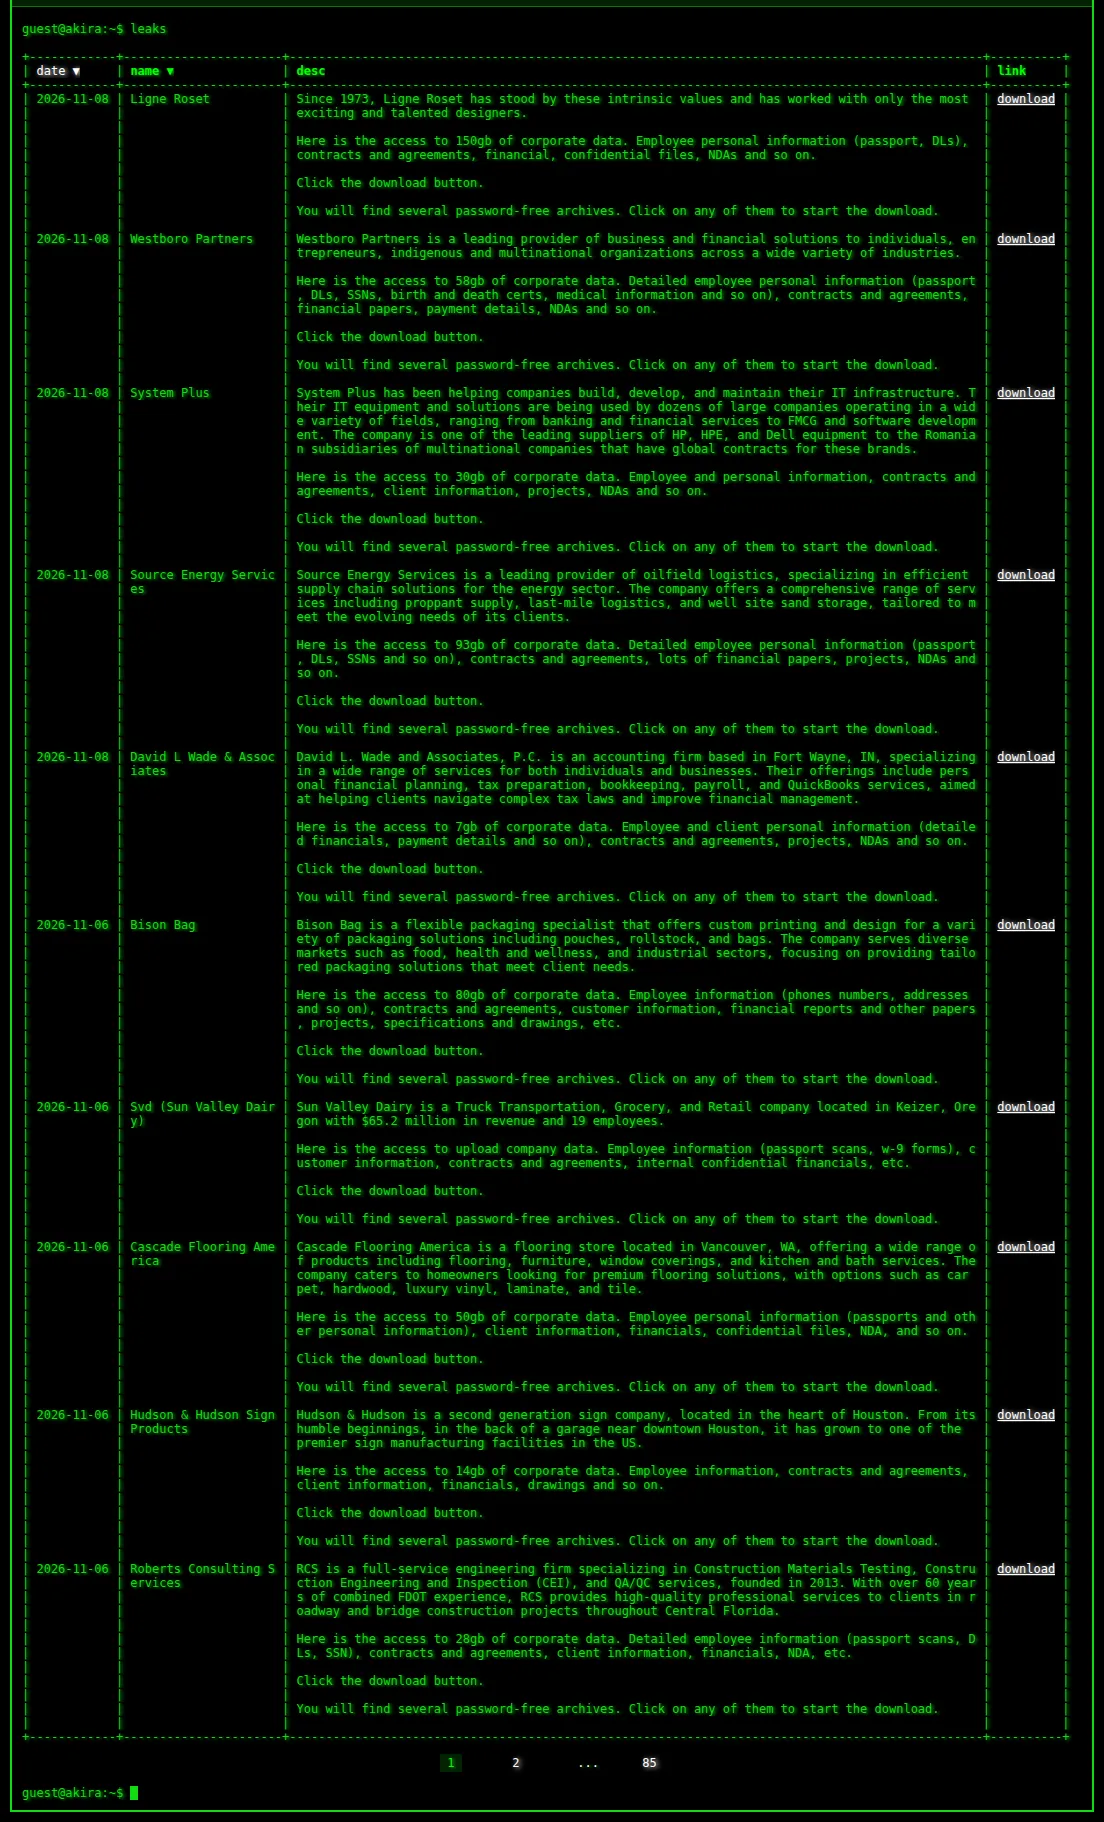
1 CAPTURED
Captured directly from the operator's leak site by our collector, last checked 2026-11-09. Verdict evidence: [akira/terminal] David L Wade & Assoc
Capture history —
2 day(s) tracked. Content is locked.
Showing the latest capture only
Unlock the 2 captures already taken.
Dark Web Exposure
Findings for dlwcpa.com
— indexed by HaveIBeenRansom.
0
found in Infostealer logs
170+
found in Traditional breaches
29+
found in Ransomware leaks
VerificationsIO_BF.7z.011
Kedr | Forum · breach
••• emails
Televerde
play · ransomware
••• emails
limeleads_breach.7z
TheUnderground - Reborn · breach
••• emails
ThePostMillennial_BF_.7z.001
Database World ROC · breach
••• emails
Email Panther @dbworldcloud.7z
DBs w MTDT · breach
••• emails
B F R e p o V 3 F i l e s · breach
••• emails
Database World ROC · breach
••• emails
+ 17 more leak sources locked
Leak volumes are locked
Sign in to reveal how many records each source exposed and the remaining 20 sources.
Legal Disclaimer:
This ransomware victim record reflects information published on the operator's leak site.
Breach.house only records what the operators themselves publish in the
open. We take screenshots of their public pages and keep the proof
material they post there, so that a listing can be verified and its status
tracked over time. We do not purchase data, we do not solicit or encourage
its publication, we do not access any private system, and we do not alter
anything we record. Nothing is offered for download here, and detailed
content is not published on this page or anywhere else on the public site:
access to it is restricted to vetted customers under contract, for
incident response, due diligence and cyber-resilience work.
Breach.house is not affiliated with, and does not act on behalf of, the
operators who publish this material. If you represent an organisation or
individual named here and want a record reviewed or removed, contact us
and we will act on it.